
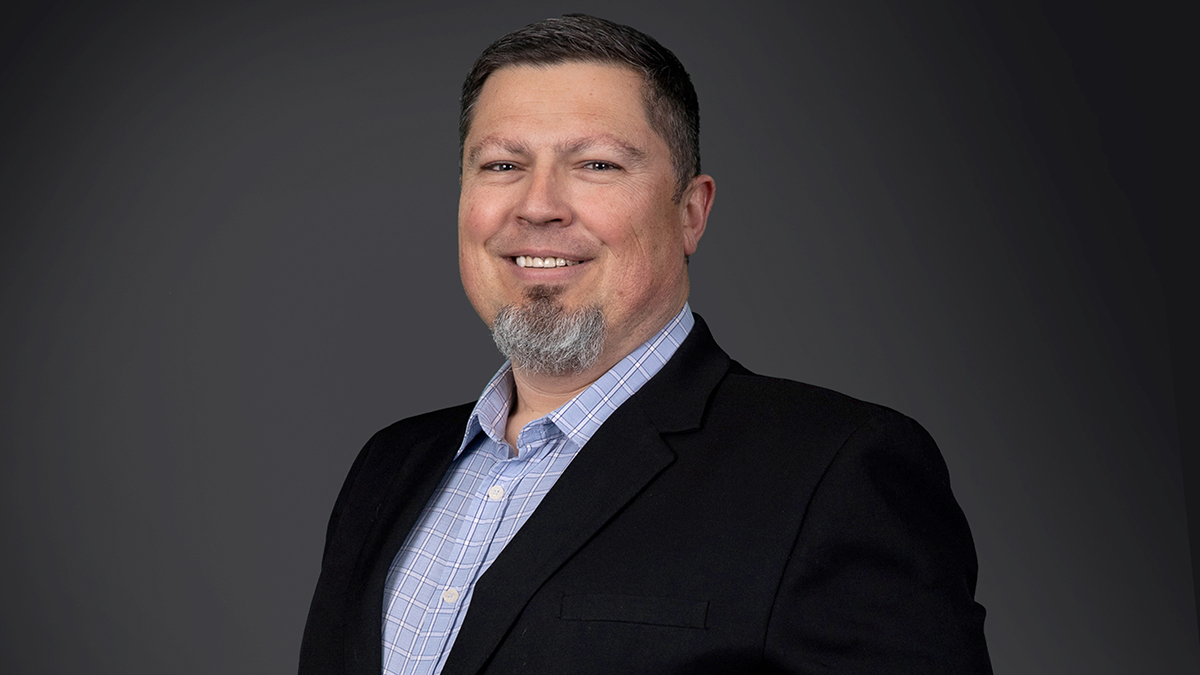
Johannesburg, 30 Oct 2026Richard Frost, head of technology solutions and consulting at Armata Cyber Security. (Image: Supplied)
In April, a South African ISP was hit by the Krybit ransomware group, which threatened to leak sensitive information unless the company met its demands. In July, Sanlam revealed that personal client information had been exposedID numbers, e-mails and contact information were leaked as a result of the breach. These companies are not alone: Liberty Group, Profmed and Rectron have had similar incidents in 2026
Liberty confirmed “unauthorised third-party access” to its systems in March; Profmed’s administrator exposed the records of more than200 000 members after attackers compromised login credentials at a supporting third-party provider in June, and Rectron, a critical supply chain distributor for resellers and vendors, including Acer South Africa, spent a week offline in July after a cyber attack it reported to the Information Regulator.
While hacks, breaches and ransomware have always been
While hacks, breaches and ransomware have always been a challenge for the organisation, the move to penetrate the business through a third-party supplier is gaining momentum. The 2025 SecurityScorecard Global Third-Party Breach Report found that 35.5% of all “data breaches originated from third-party compromises”, an increase of 6.5% from the previous year. And the reason behind this trend? Companies have become increasingly reliant on third-party service providers and solutions to do business, and in the process have accidentally left the company doors wide open.
E-mail sits with a cloud provider, records are in a hosted CRM environment, subcontractors are building systems and service providers are handling maintenance and construction. Every one of these relationships is very normal and expected in the modern enterprise, but companies aren’t always making sure that these third-party suppliers have implemented rigorous security controls.
The entry points used by the attackers are also stunningly simple. For example, a company could be using a third party to build an extension on the office, and that third party could be compromised. When the job has been completed, they e-mail an infected invoice to the company, which then opens it and falls victim to the attack. Each step is something companies do every day, and that’s exactly what the attackers are counting on. Firewalls and endpoints weren’t compromised; the infection simply travelled along a relationship that was already trusted.
The moral of the security story
The moral of the security story? Companies trust too easily and it is now time to rethink how and who enterprises trust to protect against the risk. If an increased number of ransomware attacks – 41.4% according to SecurityScorecard – come through a third party, then companies need to start assessing their suppliers and holding them to the same security standards as they do their own systems.
However, the instinct to demand the same paperwork from every vendor isn’t the right way to approach the problem. Paperwork only inspires apathy and box-ticking and usually gets ignored. Instead, security standards need to scale with the supplier through zero trust principles designed specifically for third-party connections, such as enforcing least privilege, implementing multi-factor authentication on all vendor logins and using identity-aware proxies. Network segmentation is also key as it places contractor and vendor access on separate VLANs or cloud accounts, minimising the risk of compromised vendors moving laterally into the core network.
It’s also important to have exit strategies or contingency plans in place for high-risk third parties, and to ensure you have a plan for when things go wrong. And yes, it is when. The trend is only set to gain momentum as attackers persistently look for the easiest way into the business, and that means third parties will remain a risk for the foreseeable future. The fix is to invest in proportionate governance and visibility so you know who your suppliers are and how they access your business, plus ensuring that you have security support and controls in place to detect and protect against unexpected intrusions. You need a mitigation playbook with zero trust access, continuous monitoring, full vendor visibility and contractual governance with support from a provider that can help you manage this architecture and turn an unmanageable problem into an enforceable technical control.
Charlote Hlangwane
Senior Account Manager
(010) 140 3720charlote@duomarketing.co.za
